Approximately 6,300 Italian schools recently received emails claiming remote-detonated bombs were hidden on-site, triggering a security crisis that standard policies are often unable to cover. This wave of mass-emailed threats has exposed a systemic vulnerability in the way educational and commercial institutions manage digital risks and their associated financial consequences. These incidents represent a sophisticated hybrid threat that utilizes malicious hoaxes to cause widespread economic and social disruption without ever resulting in tangible physical damage. Because traditional insurance frameworks are built around the concept of “physical loss,” these events fall into a problematic gray zone where the costs of evacuations, police responses, and lost operational hours are often unrecoverable. This has created a significant protection gap, leaving businesses and schools to shoulder the heavy financial burden of a security crisis that exists entirely in the digital and psychological realms.
Massive Disruptions: Education Systems Under Pressure
The scale of the disruption reached a frightening peak when a massive coordinated campaign targeted the Italian education system, sending thousands of institutions into a state of emergency. Schools from Rome to Milan were forced to enact emergency protocols after receiving detailed messages claiming that explosive devices were hidden in plastic bags and could be triggered remotely. The response was immediate and chaotic as hundreds of schools were fully evacuated, leading to a ripple effect that paralyzed local economies. Parents were forced to abandon their jobs mid-day to collect their children, and emergency services were stretched thin as police conducted massive searches of school grounds. This event clearly demonstrated how a single, well-crafted digital communication could bypass physical security measures and effectively shut down critical public infrastructure across an entire nation within a matter of hours, causing millions in indirect economic losses.
While Italy faced a widespread physical response, the United Kingdom and Ireland encountered a similar onslaught but adopted a markedly different tactical approach. In these regions, police authorities and government agencies analyzed the threats and largely assessed them as non-credible hoaxes, advising many schools to remain open while maintaining heightened vigilance. This contrast in response highlights the varying levels of national resilience and the difficulty of establishing a standardized protocol for digital threats. Despite the calmer reaction in the UK, the psychological impact on students, faculty, and parents remained significant. These coordinated efforts to spread anxiety and test the resilience of public infrastructure through digital means serve as a reminder that the goal of modern hoaxes is often not physical destruction but rather the creation of persistent social instability and the exhaustion of public resources through repeated false alarms.
Coordinated Campaigns: Targeting Global Transportation Infrastructure
These school-focused threats were not isolated incidents but rather part of a larger, multi-industry campaign that previously targeted the aviation and maritime sectors with similar precision. High-profile incidents included threats against multiple international flights and a major cruise ship, leading to significant airport closures and flight diversions near Warsaw and other European hubs. In one particularly intense situation, an Aer Lingus flight traveling from Dublin to Rome required an emergency escort by French fighter jets and was forced into an unscheduled landing in Normandy for extensive security screenings. These operations require a level of coordination and technical knowledge that suggests a departure from traditional “crank calls,” moving instead toward a sophisticated form of harassment that mimics the tactics of state-sponsored actors. The resulting disruptions to global travel schedules and the associated costs for airlines and airports were staggering, yet they were triggered by nothing more than a series of malicious emails.
The sophisticated tactics observed in these campaigns mirror previous hybrid warfare strategies that have been linked to state-sponsored entities looking to destabilize Western societies. By using pseudonyms and fictional organizations like the “Vilayat of Misoginistan,” the perpetrators create a layer of deniability while still achieving their objectives of causing chaos. This type of activity is part of a broader spectrum of destabilization efforts where the intent is to undermine public confidence in safety and security systems. Because these threats do not involve actual explosives, they circumvent many traditional counter-terrorism measures, forcing security agencies to reevaluate how they prioritize and respond to digital communications. The persistence of these campaigns suggests that malicious actors view hoaxes as a low-cost, high-impact tool for infrastructure disruption that can be deployed repeatedly with minimal risk to the sender but with massive financial consequences for the targets.
Policy Limitations: The Challenge of Damage-Based Insurance
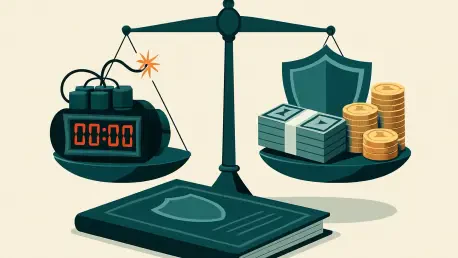
A fundamental problem for schools and businesses today is that traditional commercial insurance is built on a foundation of physical damage triggers. Most business interruption policies are designed to pay out only if there is tangible property damage to the insured premises, such as fire, flood, or a physical explosion. Because an emailed bomb threat is a non-physical event that results in disruption without any actual destruction, the business interruption section of a standard policy typically fails to respond to a claim. This leaves a massive financial hole for organizations that must close their doors or evacuate their staff. The loss of revenue during the closure, the costs of hiring specialized security consultants to sweep the building, and the legal liabilities associated with a disrupted schedule are all expenses that the policyholder must often pay out of pocket since the “trigger” for the insurance was never met.
Even when organizations are forced to evacuate by local authorities, the resulting financial losses remain largely uninsured due to these specific wording requirements. For example, an airline diversion caused by a hoax can cost hundreds of thousands of dollars in wasted fuel, additional landing fees, and passenger rebooking costs, yet hull and liability policies usually only respond if there is physical injury to passengers or actual damage to the aircraft. This discrepancy highlights a growing obsolescence in traditional insurance models that have not yet fully adapted to the realities of modern security challenges. As hoaxes become more frequent and more disruptive, the lack of coverage for “disruption without damage” represents a critical vulnerability for the education, retail, and hospitality sectors. Organizations are increasingly finding themselves in a position where they must absorb the costs of wasted operational resources and lost productivity, even when they are following all recommended safety procedures.
Navigating Definitions: The Intersection of Terrorism and War
Specialized terrorism insurance offers some potential relief for institutions facing these threats, but navigating these policies requires a deep understanding of complex legal definitions. In certain regions, government-backed schemes such as Pool Re in Great Britain have expanded their offerings to include non-damage business interruption, which can theoretically cover the denial of access to a property due to a threat or a hoax. However, this coverage is almost always contingent upon the incident being officially certified as an “Act of Terrorism” by high-level government authorities, such as the Treasury. This certification process can be slow and is often based on the perceived intent of the perpetrator. If an incident is not officially labeled as terrorism, the policyholder may still find themselves without coverage, even if they have paid for specialized protection, making the recovery of losses an uncertain and arduous process for many businesses.
Attribution plays a critical role in determining whether a policy will pay out or if a “war exclusion” will be triggered to void the claim. If a hoax campaign is eventually linked by intelligence agencies to a hostile state actor rather than a traditional terrorist group, insurers may argue that the event constitutes an act of war or a state-sponsored cyber operation, both of which are common exclusions in many policies. This creates a precarious situation where the financial survival of an affected business depends entirely on the legal and political classification of the perpetrator. Whether the sender of a threatening email is viewed as a lone wolf, a local criminal, or a foreign agent can change the entire insurance landscape for the victim. This complexity underscores the need for clearer policy language that addresses the hybrid nature of modern threats, where the lines between criminal activity, terrorism, and state-sponsored disruption are increasingly blurred.
Strategic Responses: Moving Beyond Reactionary Measures
The disparity between national responses to these hoaxes highlighted the critical importance of standardized protocols and robust threat assessment frameworks. UK government guidance, such as the programs offered through ProtectUK, encouraged organizations to judge the credibility of a threat before taking drastic measures like full-scale evacuations. By establishing clear criteria for what constitutes a credible threat, many institutions were able to avoid the massive economic and social costs of unnecessary closures while still maintaining a high level of safety. For school administrators and business owners, the stakes were incredibly high; underreacting to a potential threat could lead to a preventable catastrophe, but overreacting to a blatant hoax created significant uninsured financial losses that threatened long-term operations. Developing the internal expertise to differentiate between these scenarios became a cornerstone of modern organizational resilience.
To successfully navigate this evolving landscape, insurance brokers and risk managers advocated for a proactive approach to addressing policy limitations. They recommended that organizations in high-risk sectors like education and hospitality engage in detailed discussions about whether their current policies included non-damage business interruption and what specific events would trigger a payout. It became essential to define whether a police cordon, a mandatory government order, or a self-initiated evacuation would be covered under the terms of the agreement. Furthermore, organizations were encouraged to maintain updated bomb threat plans that followed the latest official government guidance to ensure that decision-makers could act decisively and defensibly during a crisis. Ultimately, the industry moved toward a model where financial protection and operational planning were integrated, recognizing that in an era of digital hoaxes, resilience was built as much on informed decision-making as it was on traditional insurance coverage.